GDPR and CCPA Compliance for Web Developers: Cookies, Consent & Data Rights
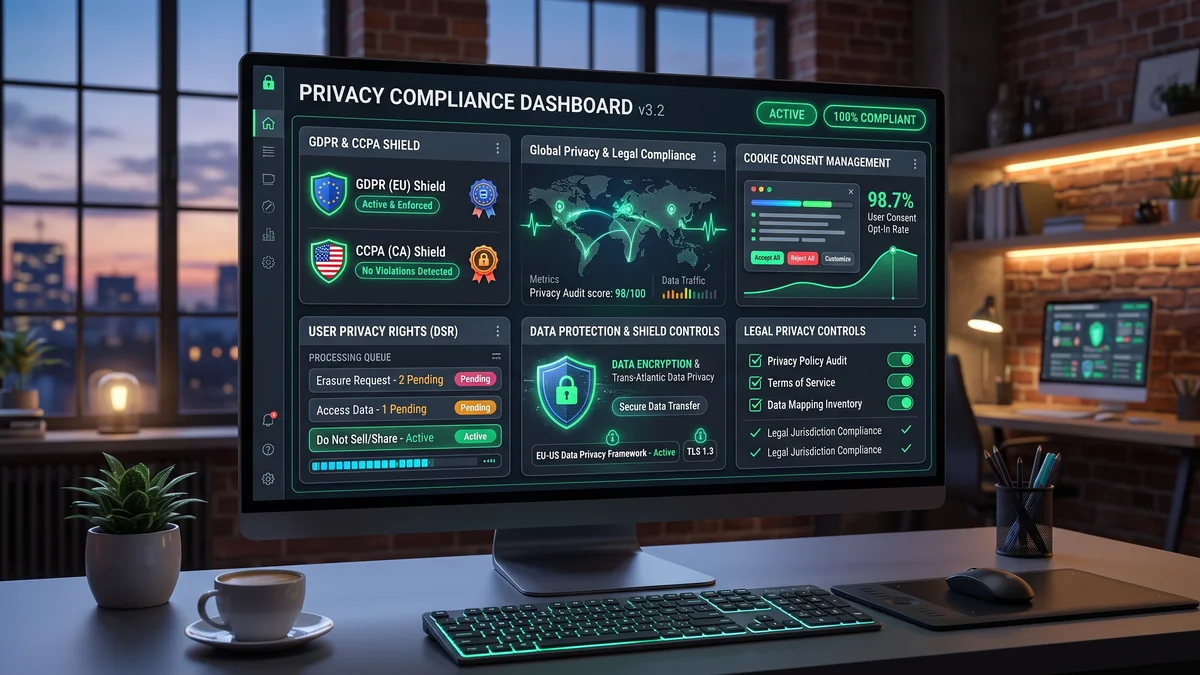
Avoid multimillion-euro fines. Learn how to architect cookie consent managers, build automated Data Subject Access Request (DSAR) pipelines, and anonymize user logs.
Technical deep-dives, software architecture paradigms, and cloud engineering strategies from our senior architects.
Avoid multimillion-euro fines. Learn how to architect cookie consent managers, build automated Data Subject Access Request (DSAR) pipelines, and anonymize user logs.
Stop relying on gut feeling. Learn how continuous discovery frameworks by Teresa Torres help product managers conduct weekly customer interviews and prioritize features.
Selecting a web development stack is a critical business decision. Compare Laravel, Node.js, Python, React, and Vue across performance, speed to market, and talent pool.
Move beyond vanity metrics. A comprehensive guide to instrumenting SaaS telemetry, measuring MRR, CAC, LTV, Net Revenue Retention (NRR), and DAU/MAU ratios.
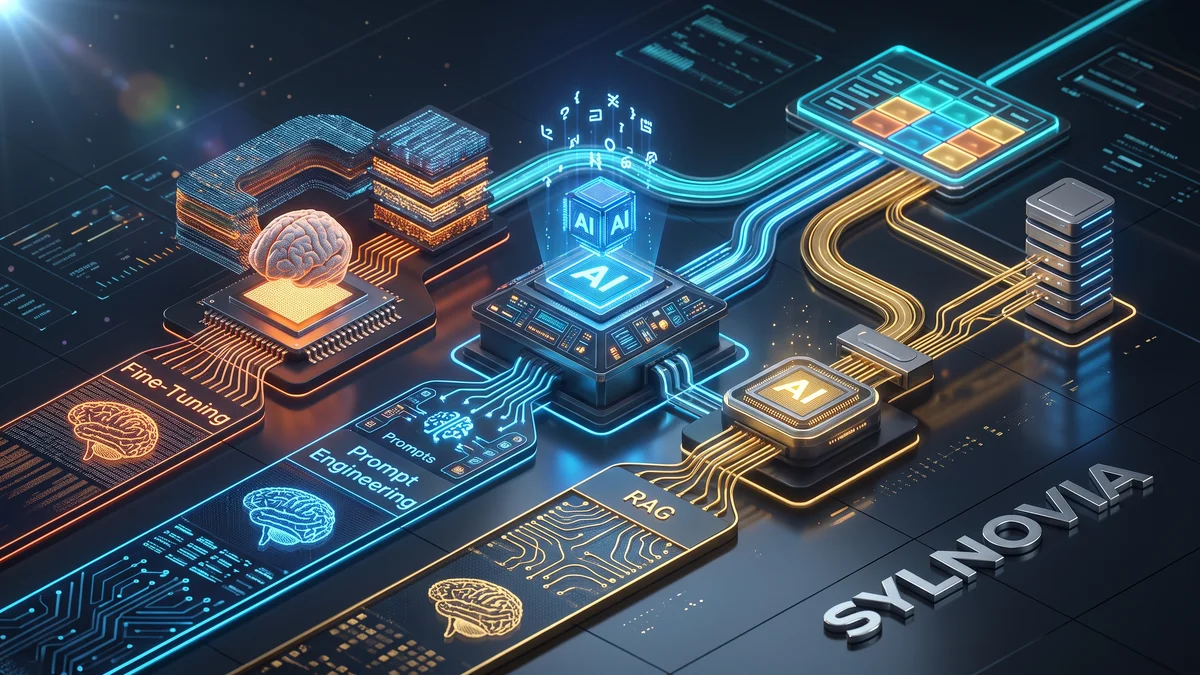
Struggling to choose between prompt engineering, fine-tuning, and RAG? Compare costs, data requirements, latency, and maintenance overhead for enterprise AI.
Slash server response times from 800ms to 40ms. Learn how multi-tier caching with PHP OPcache, Redis memory stores, and Cloudflare Edge CDNs supercharges scale.
Building real-time chat, notifications, or live dashboards? Compare WebSockets, SSE, and long-polling across server resource consumption, latency, and firewall traversal.
Don’t let Apple or Google delay your launch. A comprehensive guide to passing App Store review: privacy manifests, IAP compliance, and test account setup.
Discover how subtle UI feedback, button states, pull-to-refresh animations, and page transitions guide users and make software feel alive.
Software is never truly "finished". Discover why proactive maintenance, security patches, framework upgrades, and SLA guarantees protect your product investment.
Stop breaking frontend apps when updating backend APIs. Learn how consumer-driven contract testing with Pact verifies integrations without running whole clusters.
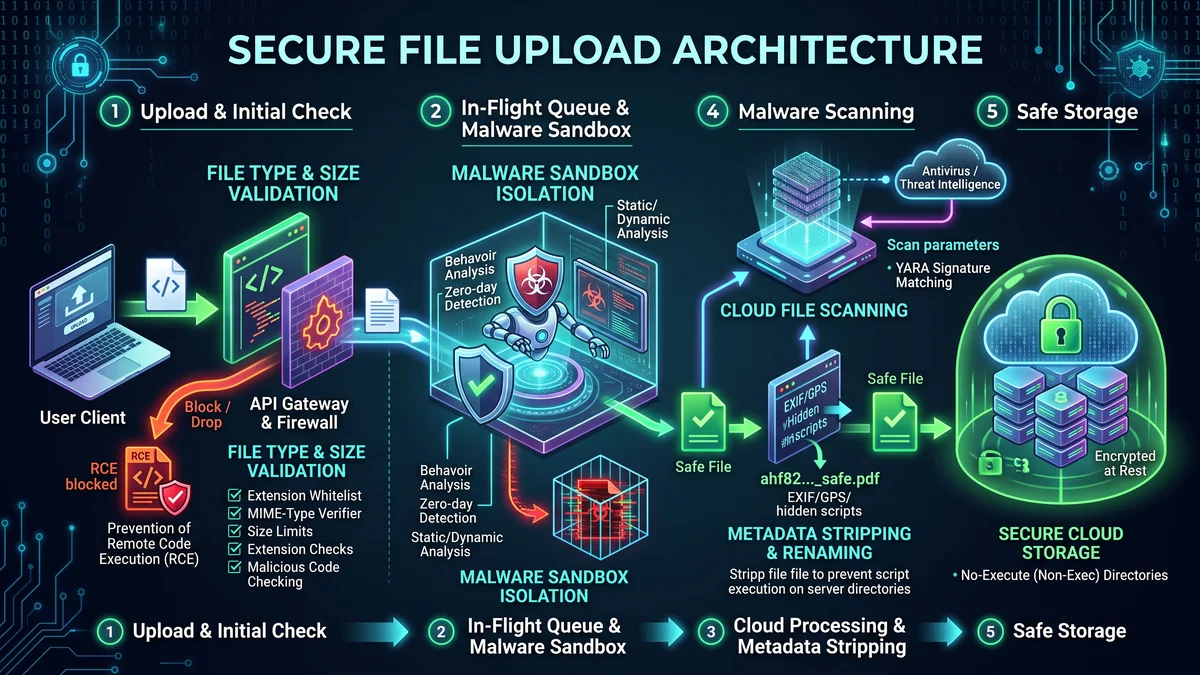
Unrestricted file uploads are among the most dangerous web vulnerabilities. Learn how to validate MIME types, re-encode images, and store uploads in isolated buckets.
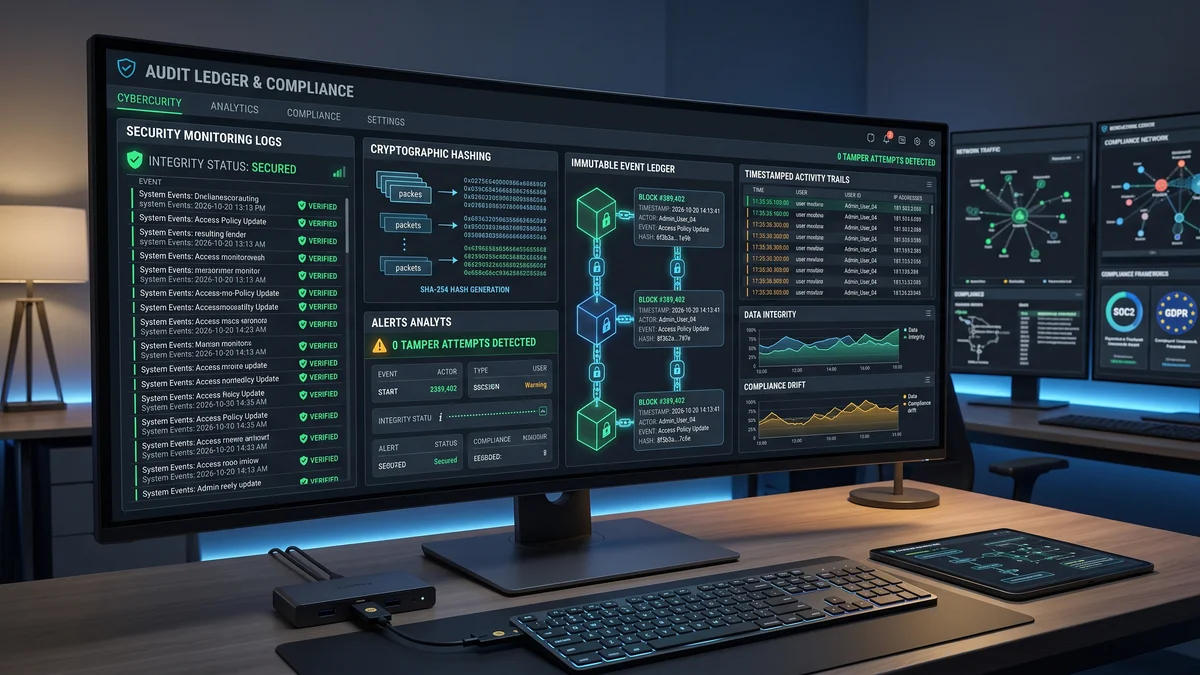
Who did what and when? Discover how to architect immutable, searchable audit logs in web applications for SOC 2, HIPAA, and internal security investigations.