
Sylnovia © 2026 · All Rights Reserved
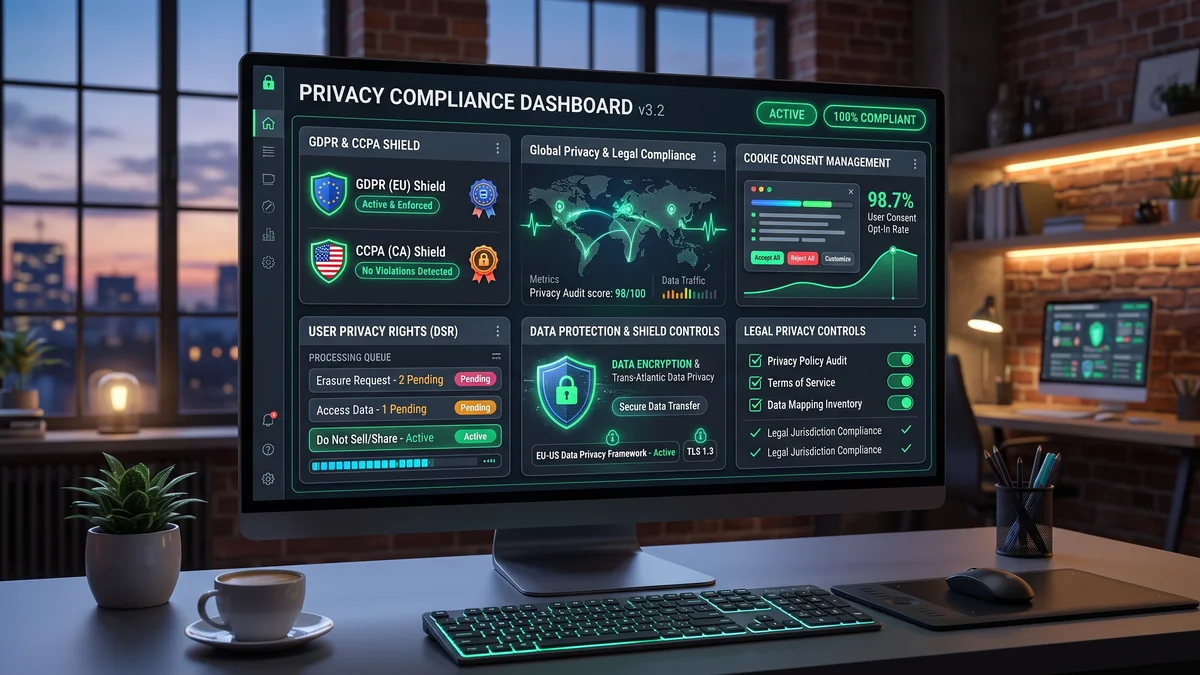
Global privacy regulations—including Europe's General Data Protection Regulation (GDPR) and the California Consumer Privacy Act (CCPA/CPRA)—have fundamentally transformed digital software engineering. Privacy is no longer just a legal document drafted by corporate attorneys; it is a technical architectural requirement that dictates how data is collected, stored, processed, and deleted.
Failing to comply with global privacy laws carries severe financial penalties: GDPR fines can reach up to €20 million or 4% of global annual turnover.
In relational databases where foreign keys link user records to historical financial invoices, deleting the user row can corrupt financial audit trails. The standard engineering solution is Cryptographic Anonymization: replace personal fields (name, email, ip_address) with anonymized hashes (deleted_user_48291@anonymized.local) while preserving transaction totals for accounting compliance.
Sylnovia designs compliant software architectures, automated data export engines, and cookie consent implementations that satisfy global privacy mandates. Partner with our privacy engineering specialists today.
Delivering deep technical insights, architectural blueprints, and digital strategy for modern engineering squads.





The Strategic Hiring Dilemma for Growing Businesses When leadership teams decide to build a custom software platform or...
The False Dichotomy of Manual vs. Automated QA In software engineering discussions, testing is often framed as an all-o...
Why Enterprise B2B Buyers Mandate SOC 2 Type II When selling software to Fortune 500 enterprises, healthcare organizati...