
Sylnovia © 2026 · All Rights Reserved
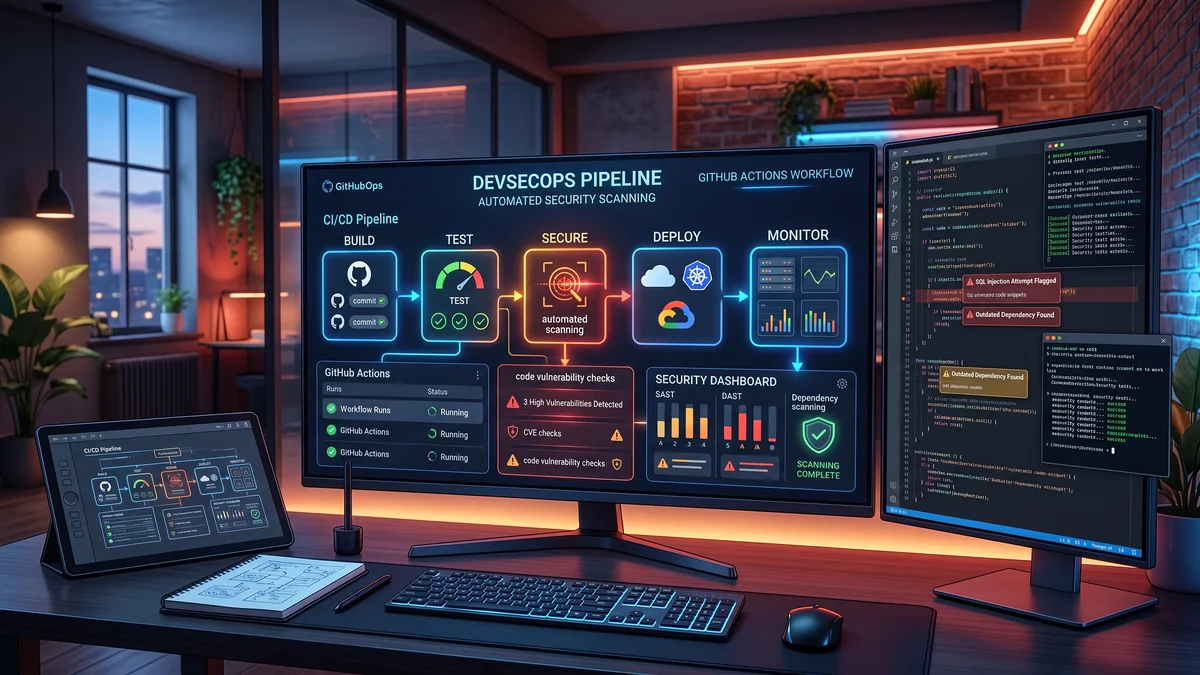
In legacy software organizations, security was treated as a bureaucratic bottleneck at the very end of the development cycle. Developers wrote code for six months, and right before launch, a security team conducted a manual review, identifying dozens of vulnerabilities that delayed release by months.
DevSecOps fundamentally transforms this workflow by "shifting security left"—integrating automated security scanning, vulnerability detection, and compliance gates directly into the developer's daily continuous integration (CI/CD) pipeline.
Developers accidentally committing AWS access keys, Stripe secret keys, or database passwords to Git repositories is one of the most common causes of catastrophic data breaches. Tools like TruffleHog or GitGuardian scan every commit and pull request, instantly failing builds if entropy analysis detects credential patterns.
Modern applications consist of 80% open-source third-party dependencies (npm, composer, pip). Tools like Dependabot and Snyk continuously scan your dependency lockfiles, generating automated pull requests when a CVE vulnerability is identified in an upstream package.
Automated source code analysis tools (SonarQube, Semgrep, CodeQL) scan source code for insecure programming patterns (SQL injection, unsafe deserialization, hardcoded secrets) before code merges to production.
Scanners (Trivy, Grype) analyze compiled Docker container images, detecting unpatched operating system vulnerabilities in underlying Linux base layers (Debian/Alpine).
Configure pipeline security gates with pragmatic severity thresholds: Break the build on CRITICAL and HIGH severity vulnerabilities; file automated tracking tickets for MEDIUM and LOW issues. Fast, automated feedback empowers developers to fix security flaws in minutes while code context is fresh.
Sylnovia helps engineering organizations automate security scanning, harden GitHub Actions pipelines, and build secure CI/CD workflows. Contact our DevSecOps team to secure your deployment pipeline.
Delivering deep technical insights, architectural blueprints, and digital strategy for modern engineering squads.





The Strategic Hiring Dilemma for Growing Businesses When leadership teams decide to build a custom software platform or...
The False Dichotomy of Manual vs. Automated QA In software engineering discussions, testing is often framed as an all-o...
Why Enterprise B2B Buyers Mandate SOC 2 Type II When selling software to Fortune 500 enterprises, healthcare organizati...