
Sylnovia © 2026 · All Rights Reserved
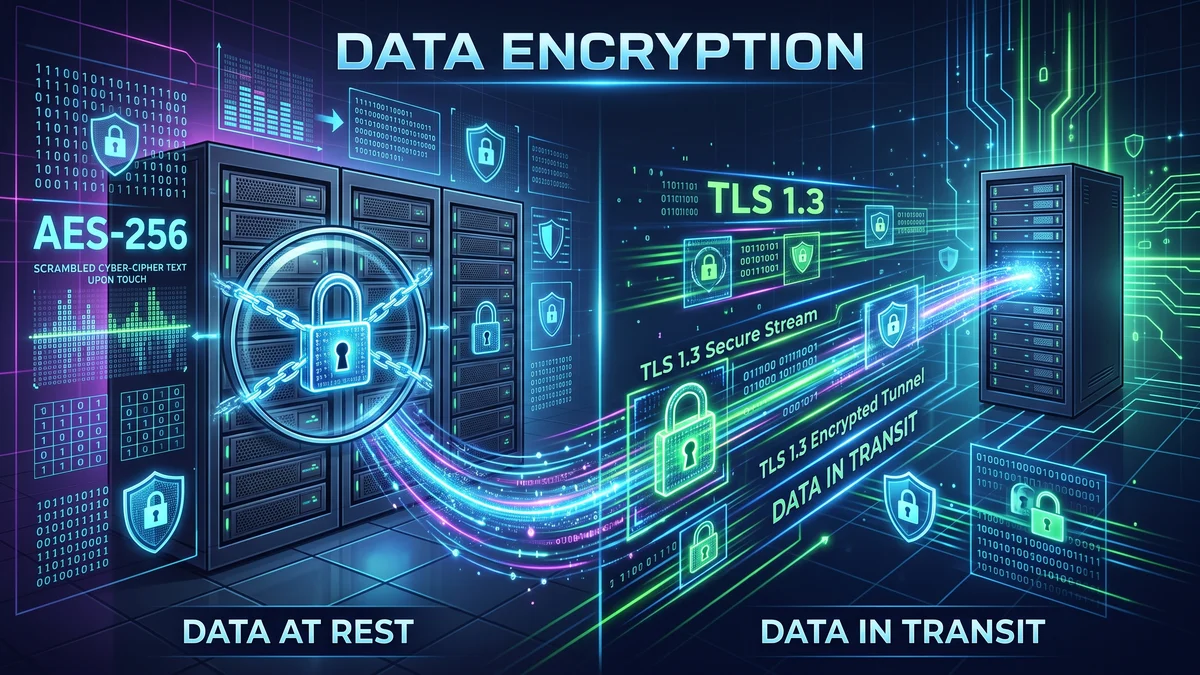
Data is the most valuable asset an enterprise possesses—and the primary target of malicious threat actors. A comprehensive data security strategy mandates that sensitive customer data, financial records, and intellectual property remain cryptographically unreadable to unauthorized parties across every stage of the data lifecycle.
This requires implementing rigorous Encryption in Transit and Encryption at Rest.
All network communication between web clients, mobile apps, and backend APIs must be encrypted over TLS (Transport Layer Security):
max-age=31536000; includeSubDomains; preload) instructing browsers to never connect to your domain over insecure HTTP.// Laravel Eloquent Encrypted Attribute Casting
protected $casts = [
'ssn' => 'encrypted',
'bank_account_number' => 'encrypted',
];Never hardcode encryption keys in source code or environment files. Manage master keys inside dedicated Hardware Security Modules (AWS KMS, Azure Key Vault, HashiCorp Vault) enforcing granular IAM access policies.
At Sylnovia, our security engineers implement defense-in-depth cryptographic architectures that comply with PCI-DSS, HIPAA, and GDPR standards. Protect your mission-critical data by partnering with our team.
Delivering deep technical insights, architectural blueprints, and digital strategy for modern engineering squads.





The Strategic Hiring Dilemma for Growing Businesses When leadership teams decide to build a custom software platform or...
The False Dichotomy of Manual vs. Automated QA In software engineering discussions, testing is often framed as an all-o...
Why Enterprise B2B Buyers Mandate SOC 2 Type II When selling software to Fortune 500 enterprises, healthcare organizati...